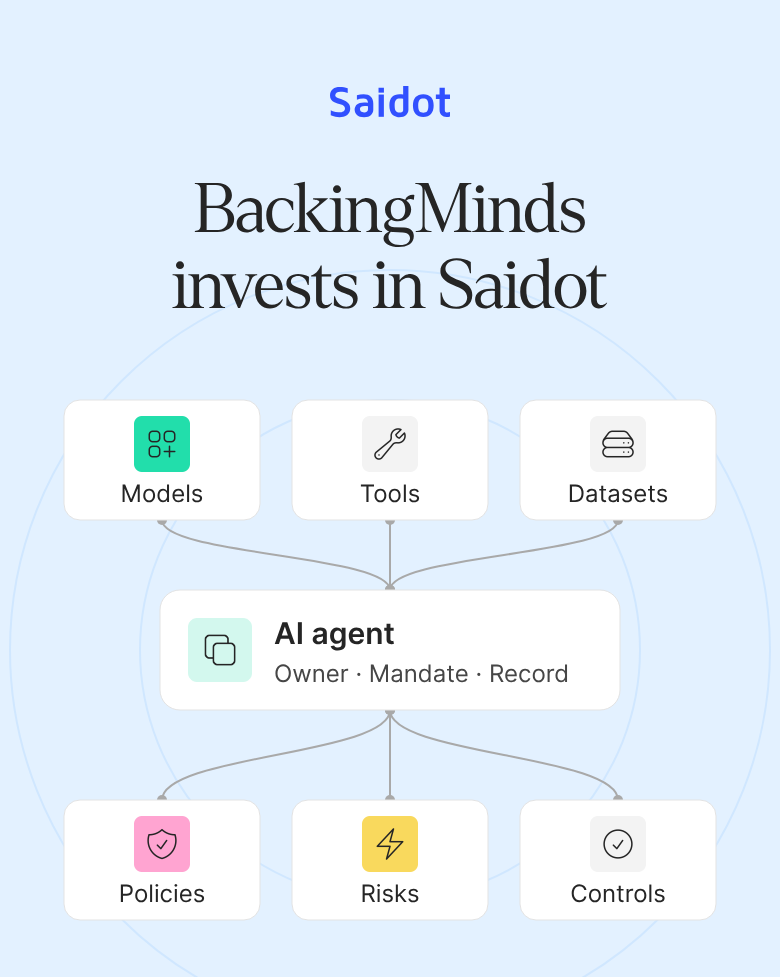
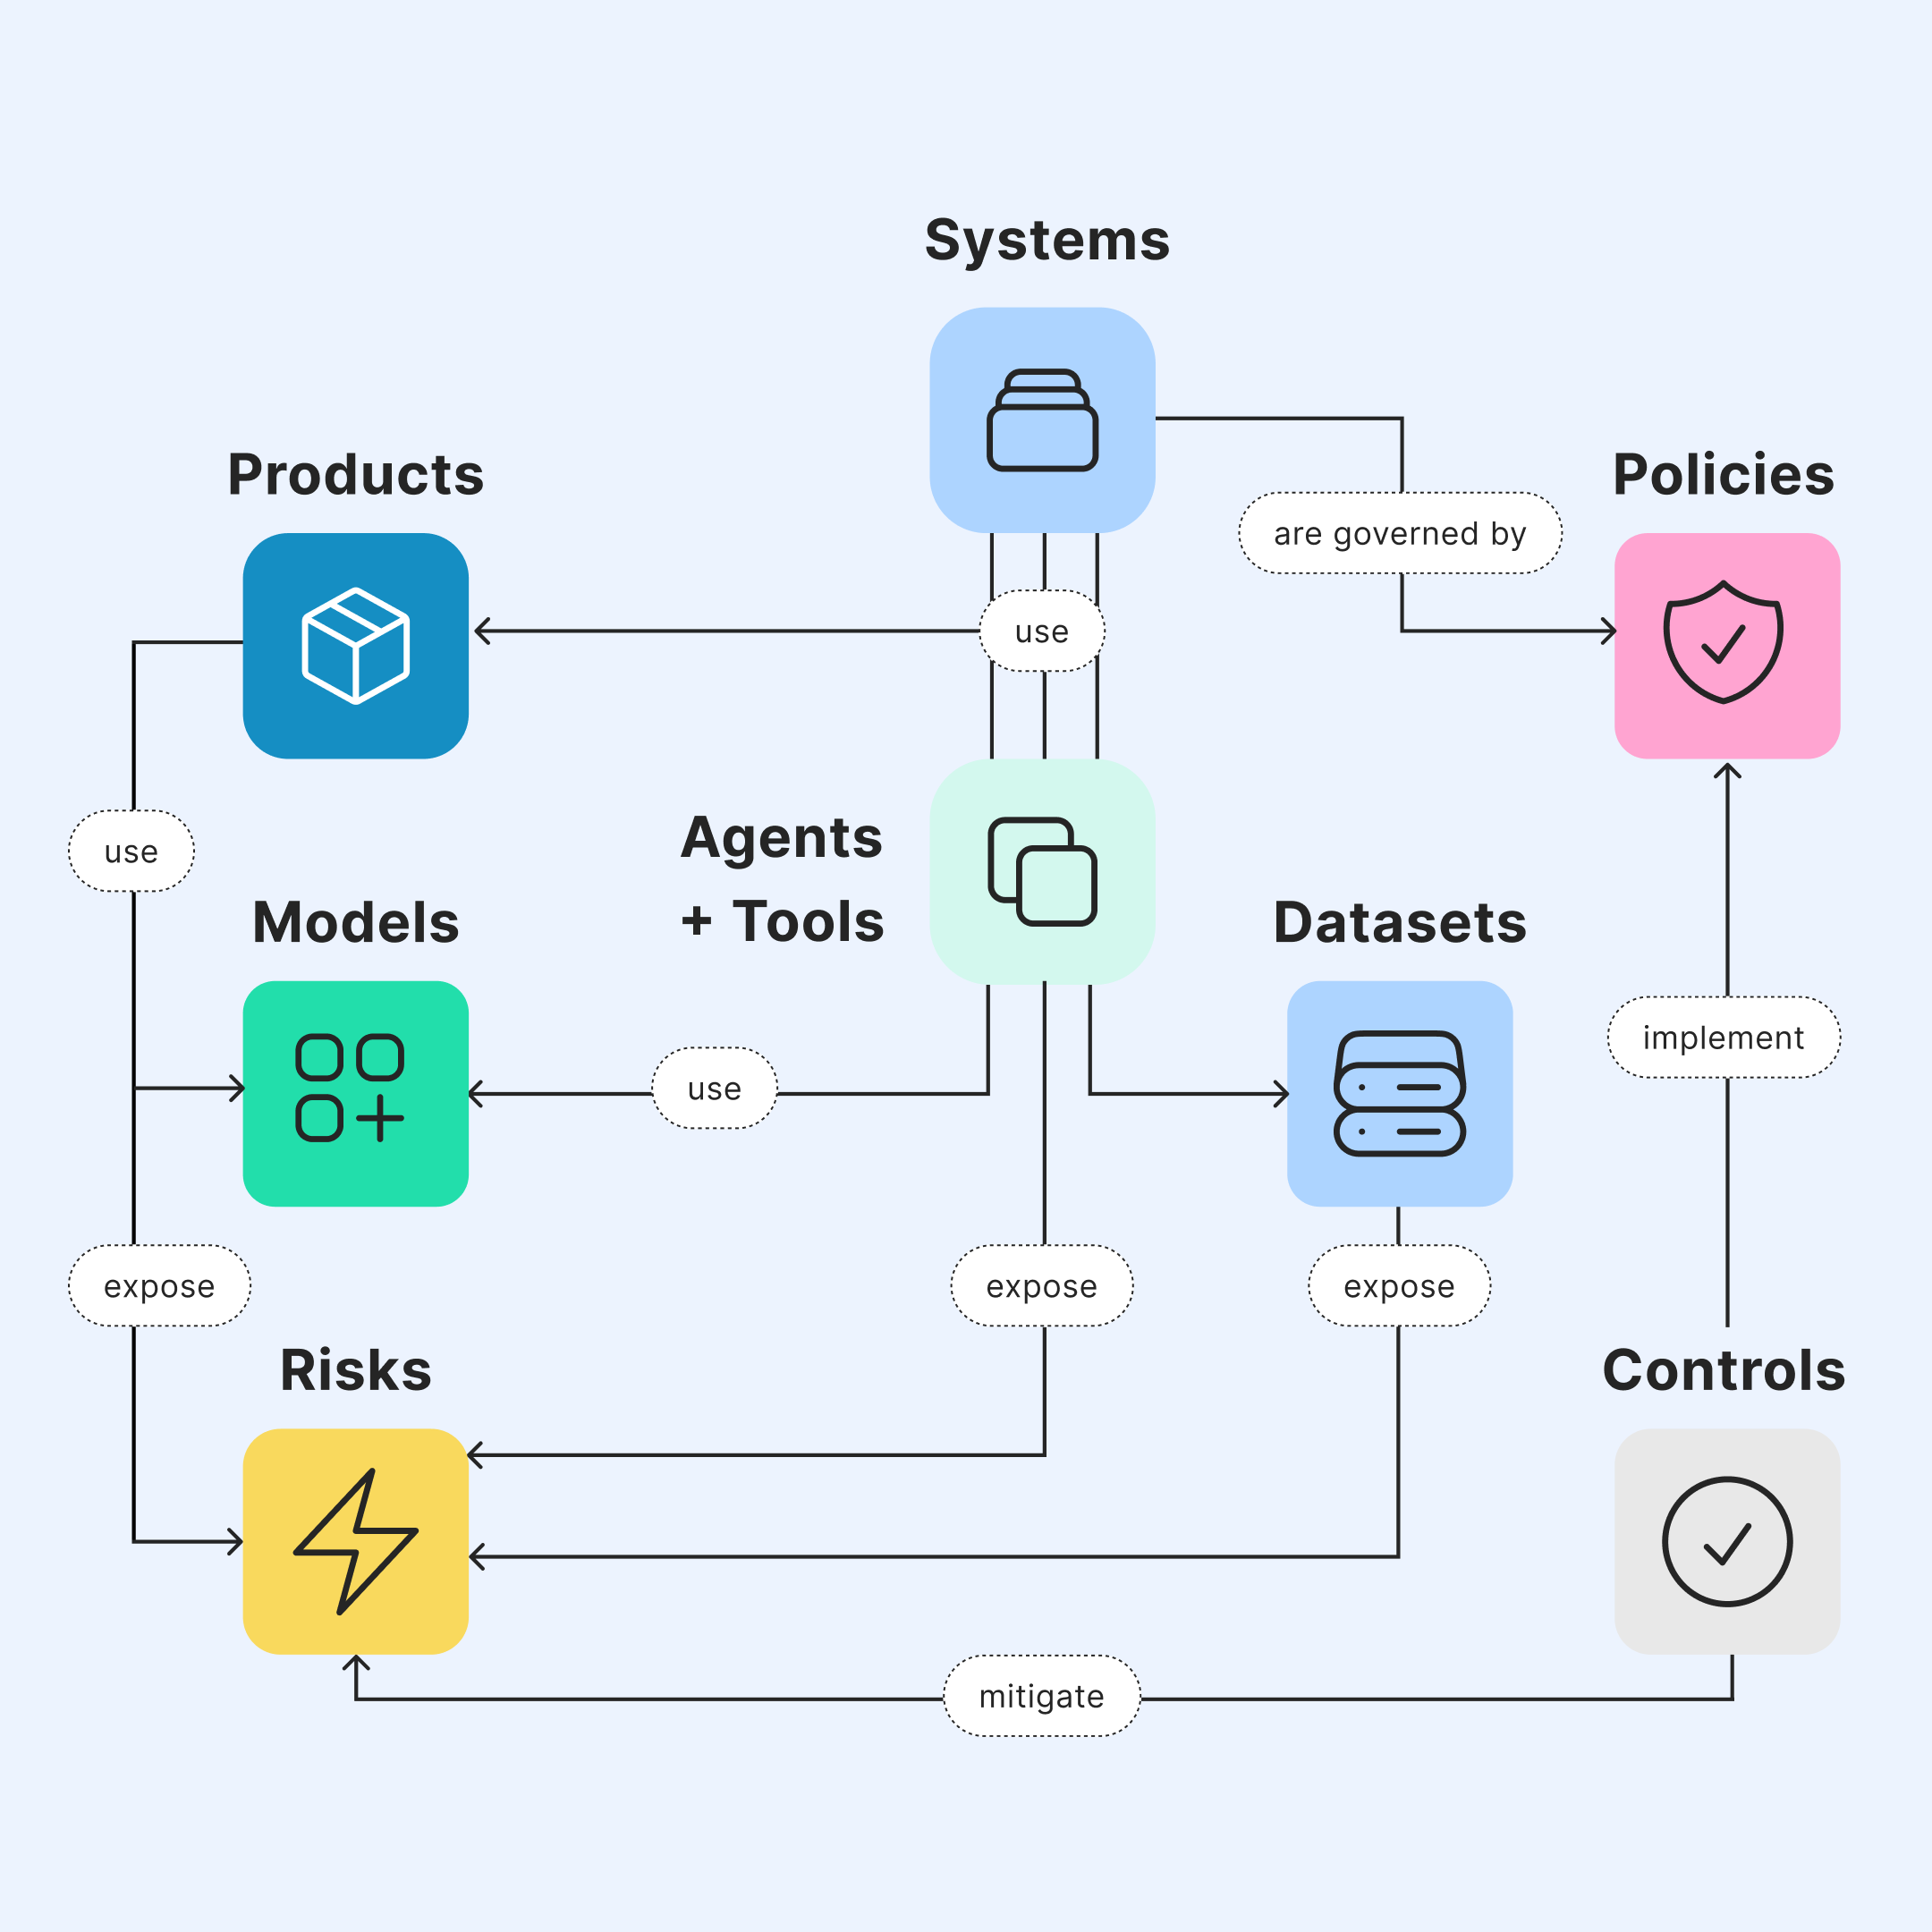
An ordinary record is a list. Saidot's AI governance record knows how everything connects and who owns each part. The graph connects systems, models, agents, tools, datasets, risks, controls and evidence.
(To see a short demo teaser, please allow marketing cookies.)
(Allow marketing cookies to see our product video.)

Models, products and regulations change often. Saidot's AI governance experts maintain the Library, and the systems that link an updated item receive the change through the graph.

Agents are both what is governed and what does the governance work, while people retain accountability. AI teams own their systems in the first line, risk and compliance set policy in the second, and internal audit provides assurance in the third.

Just like in any natural sciences, we need to run tests to verify how models perform and behave. Saidot generates testing and red-teaming plans from a system's risks, and evaluation results feed back into risk decisions.

You don't need to share your business secrets but should be open about how your AI affects users, customers, and other stakeholders around you. Saidot enables you to publish transparency reports directly from your documentation, avoiding double work.
The board decides how much room AI gets. With overview and evidence, you can give AI more room, and the AI investment starts to pay off.
Set rules once that are inherited. Review exceptions instead of everything. Internal audit has traceability and evidence linked to every agent.
Register agents directly from your own tools, stop answering the same questions again, and reach production faster.

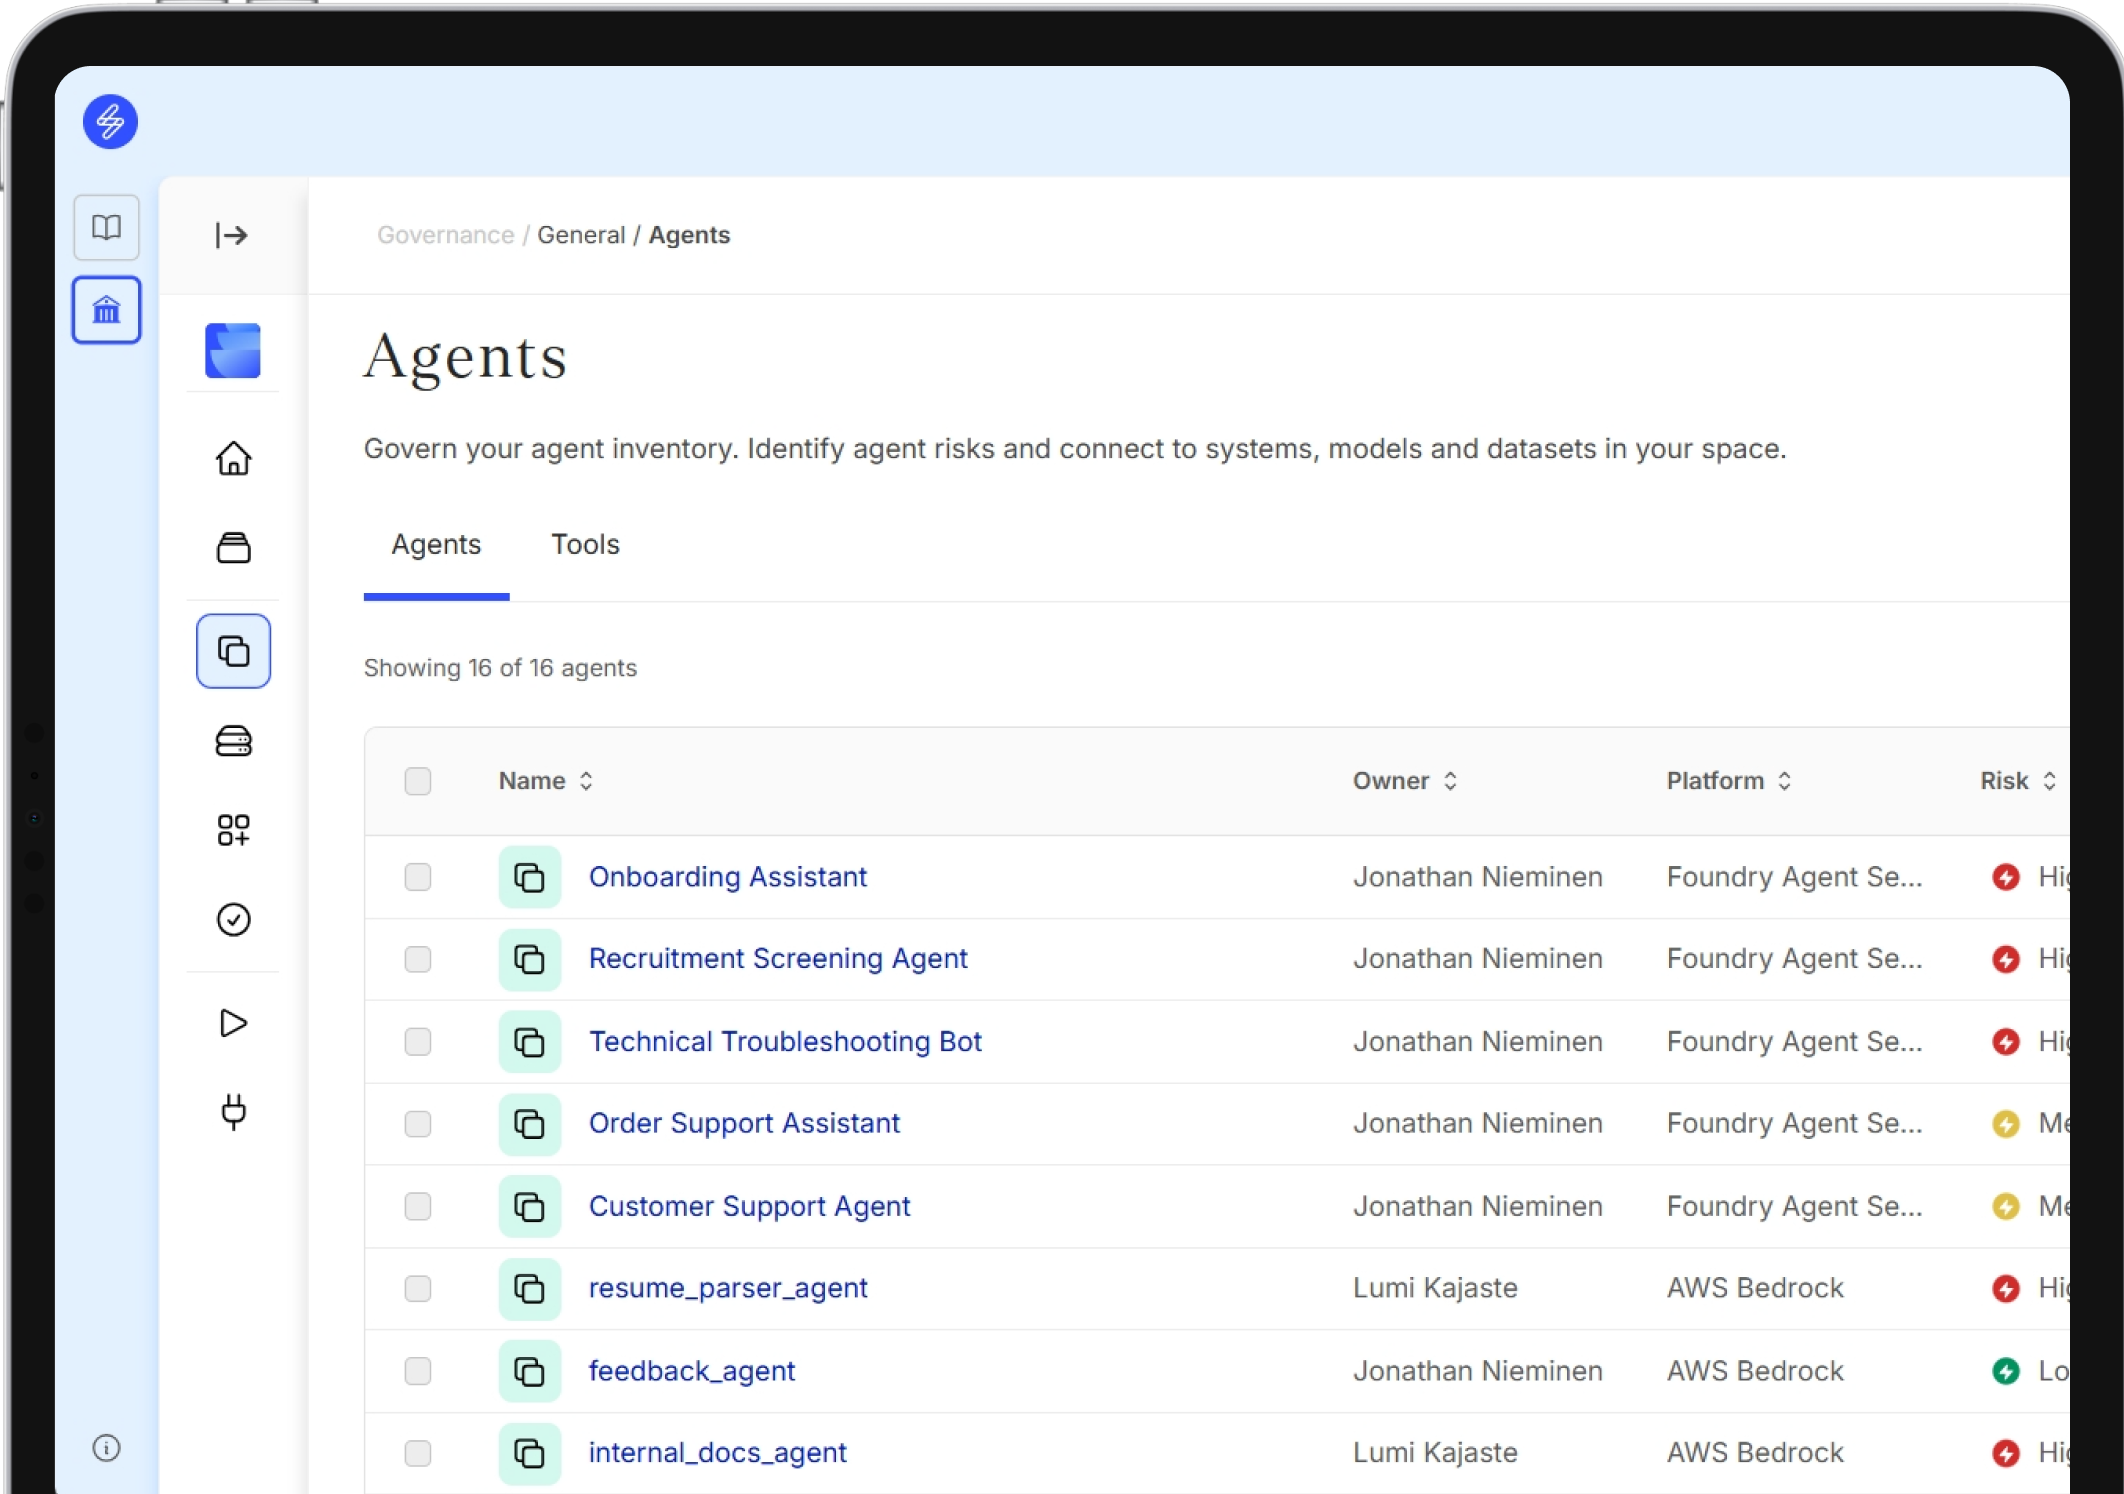
Have every AI agent, system, model, and dataset in one place. Models and agents sync from your AI development platforms, so your inventory remains current.
Learn more about the AI inventory

Saidot is built for governing AI agents. Deploy knowing their risks and exactly what they can do. Every tool an agent can reach is risk-classified, not just the model.
Learn more about agent governance

Do governance with your own AI agents in the flow of work. Three MCP servers let your own AI assistants register agents and draft risk assessments.
Learn more about agent-first AI governance

Identify, evaluate, and treat risks. Right-sized risk management grounded in the EU AI Act, ISO and NIST standards, and 110+ other policies.
Learn more about risk management

Map controls to policy requirements, and linked systems and agents inherit them.
Learn more about compliance and controls

When everything's connected, governance keeps pace; around 95% of the platform is controllable via REST API.
Learn more on configurations

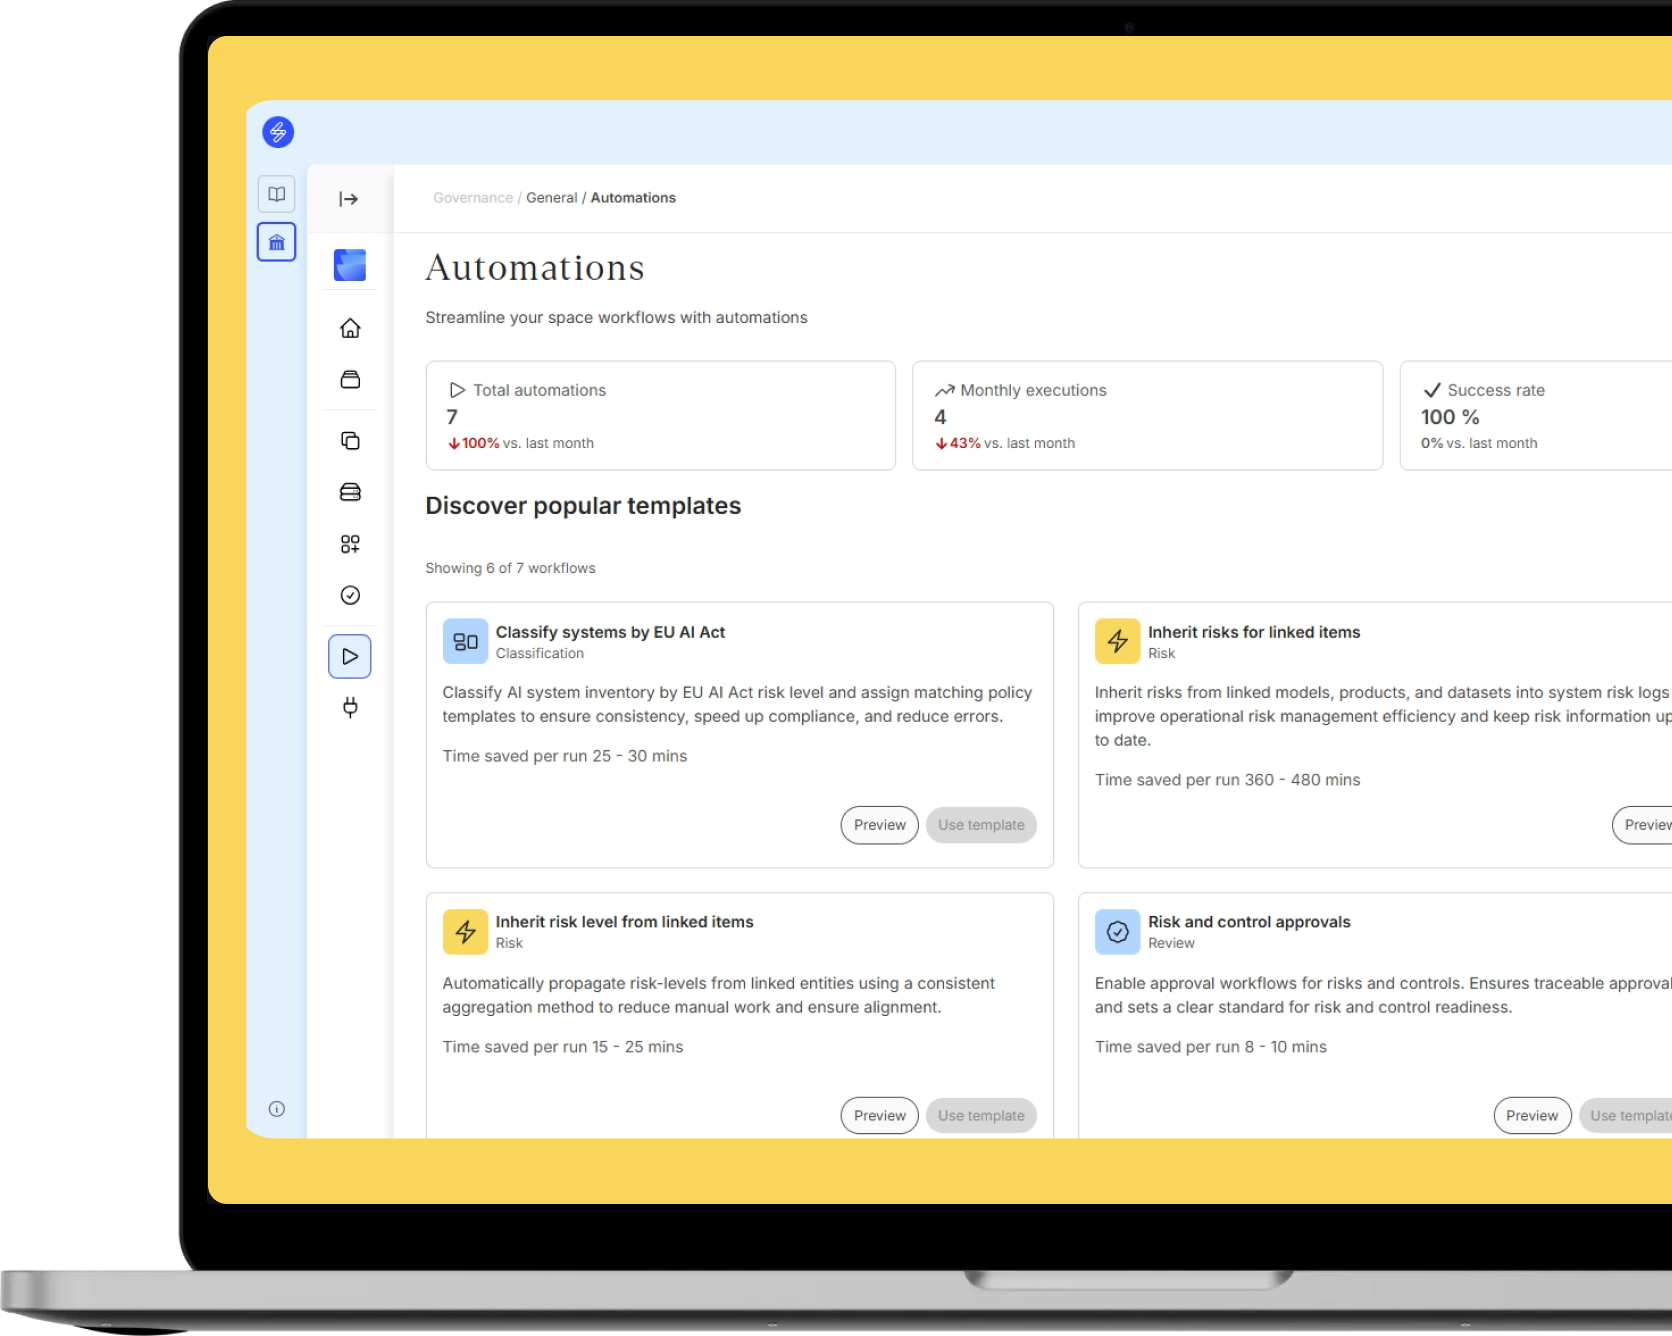
Govern your AI in production. Route events from your AI stack into reviews, incidents and risk-level changes.
Learn more about event-driven governance

A complete, traceable record of your governance, ready for any audit or review.
Learn more about compliance

Build trust in your agents. Publish what your stakeholders need to know, generated from your governance data.
Learn more about transparency reports

Connect technical testing to governance, so evaluation results inform real risk decisions.
Learn more about evaluations
Sarah Bird, CPO, Responsible AI at Microsoft
Learn more in our blog
Using our handbook, you’ll govern AI at the speed you build it, reuse work across models and agents, and stay EU AI Act ready.